Gözcü · By use case
Meet your monitoring obligation with records you can defend
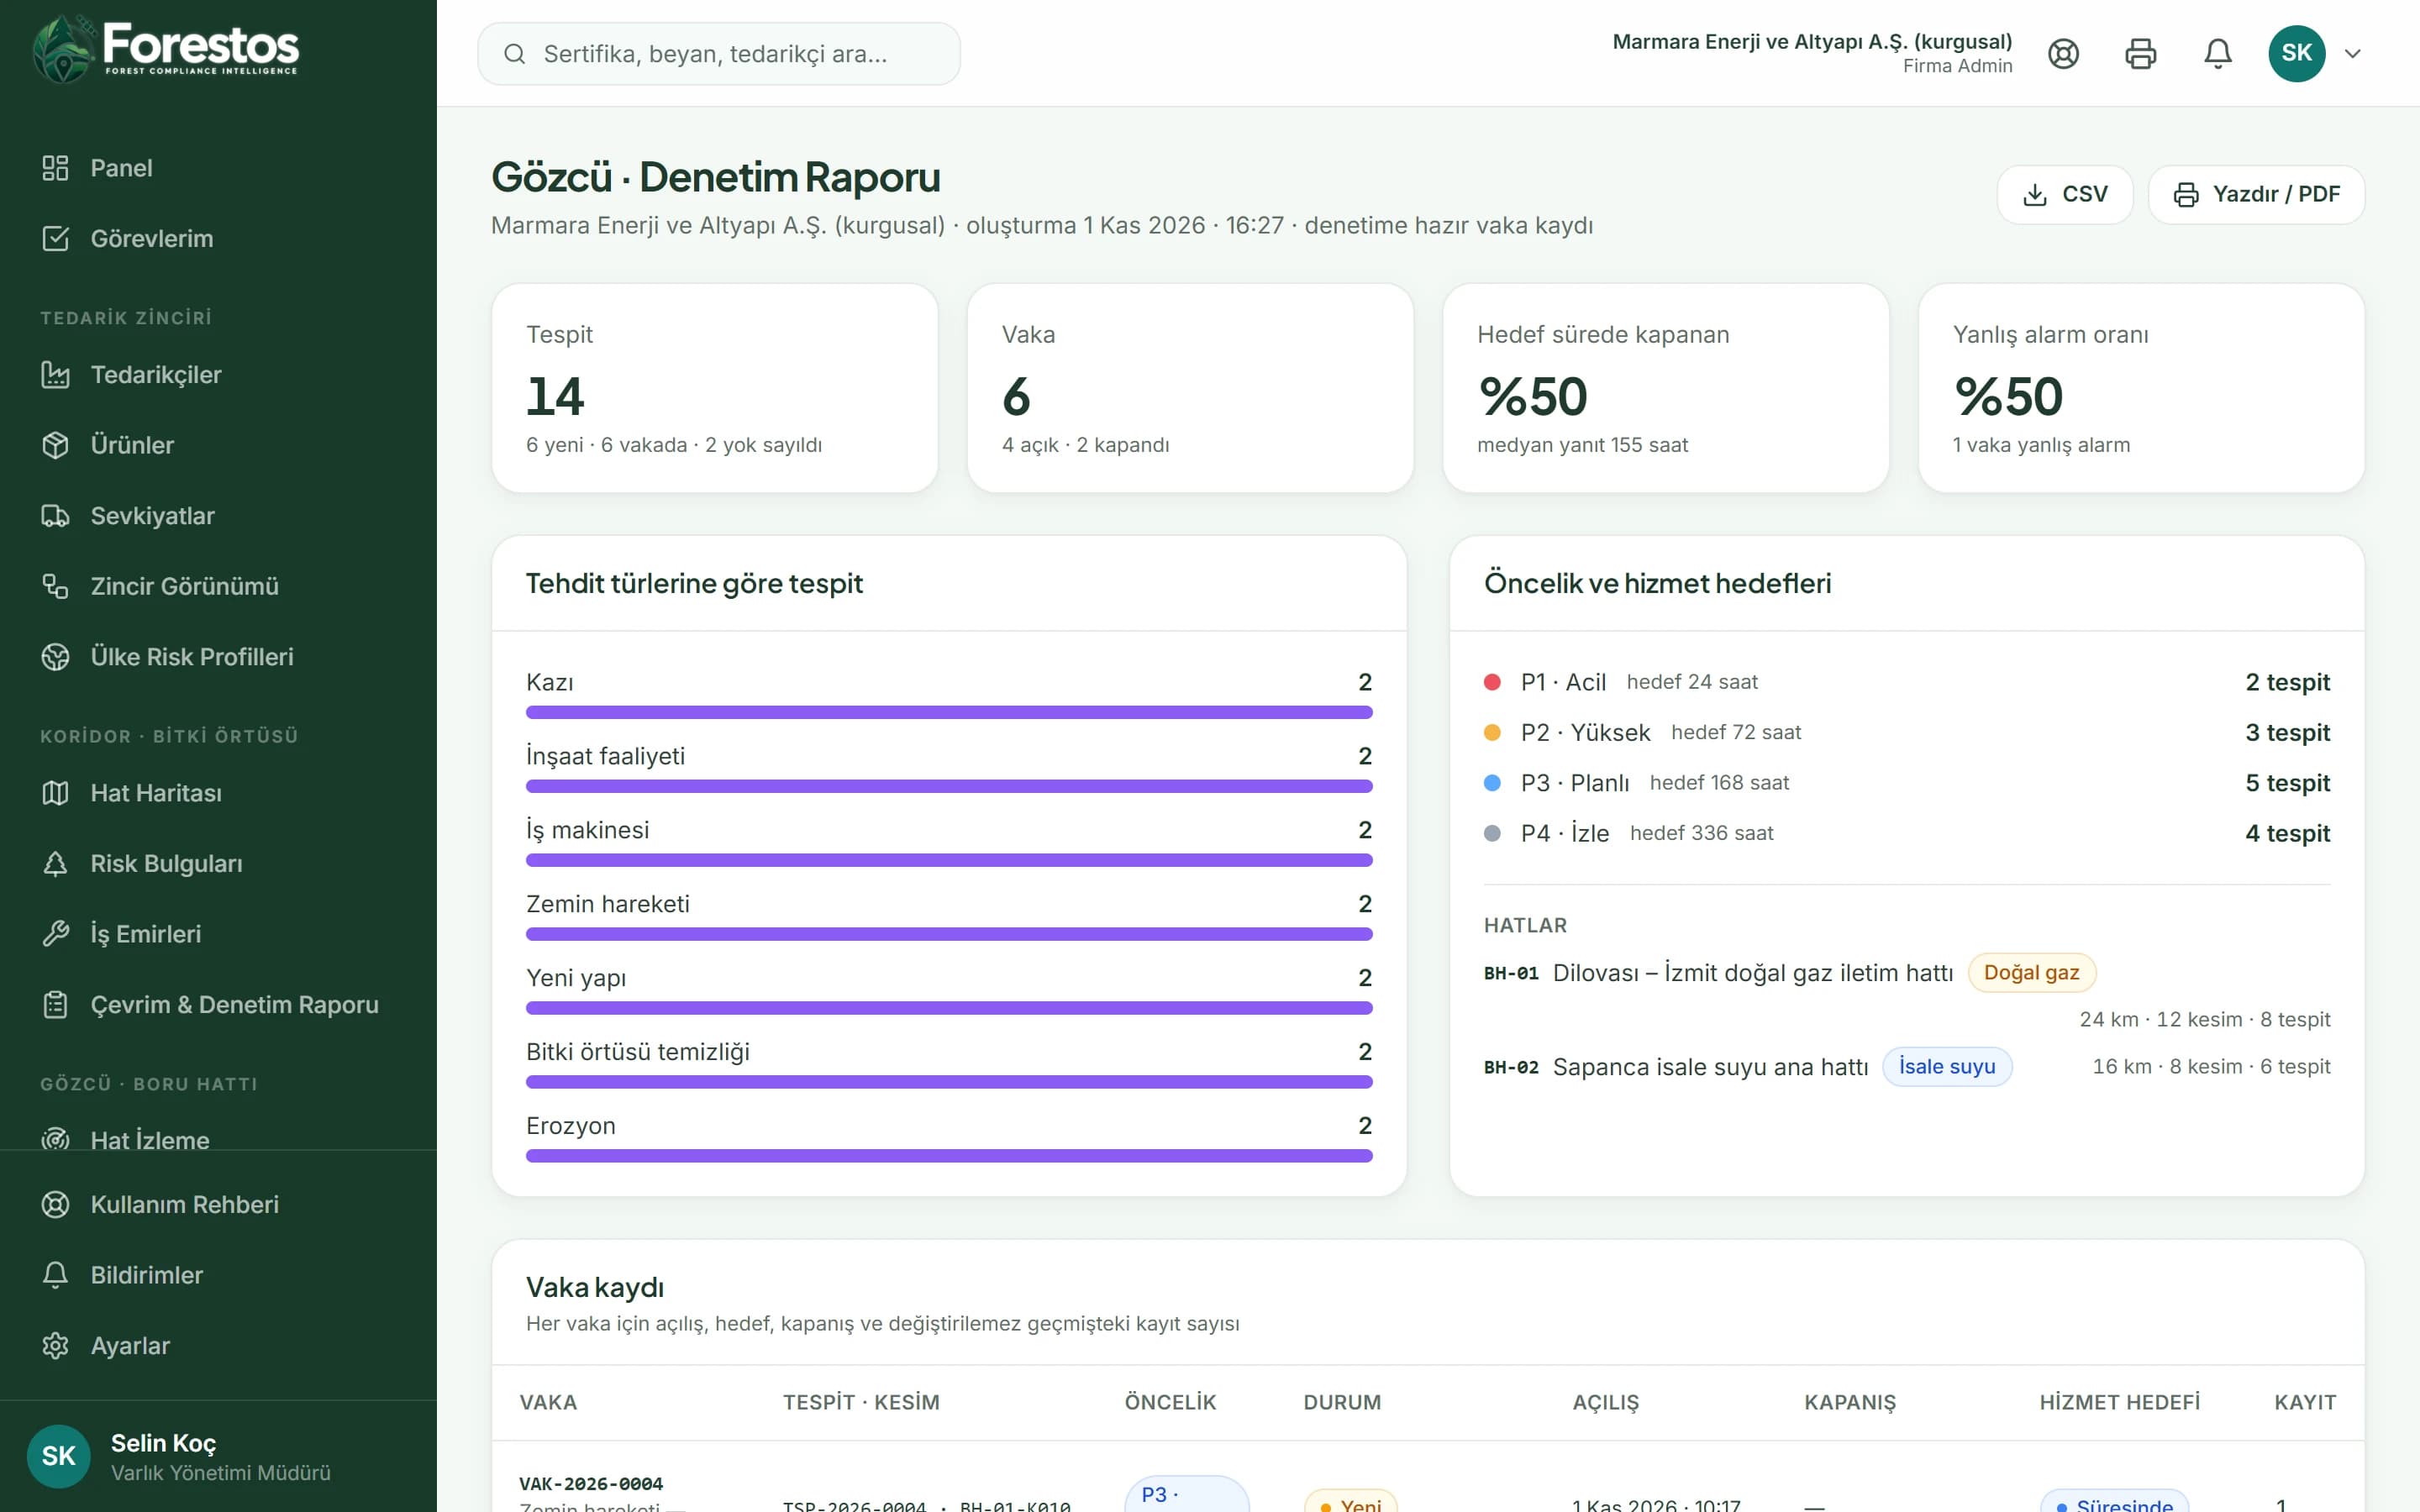
Present your detection and case records in an audit-ready report; show who did each step, and when.
Frameworks we map to
- EUDR
- FSC®
- PEFC
- SBP
- ISO 14001
- GRI
- KVKK
- GeoJSON
- EU Information System (TRACES)
- WGS84
- CSV / REST API
- ISO 27001 control mapping
What auditors ask
When did you see it?
The date of first sighting, and the evidence.
What did you do?
Assignment, field check, mitigation.
How quickly?
Compliance with the target time.
Audits with Gözcü
Gözcü's features work together in this scenario.
Audit Reports
Prove compliance with defensible records
The report is built only from the detection and case records in the app; every figure can be traced back to its record.
Case Management
Turn insight into action
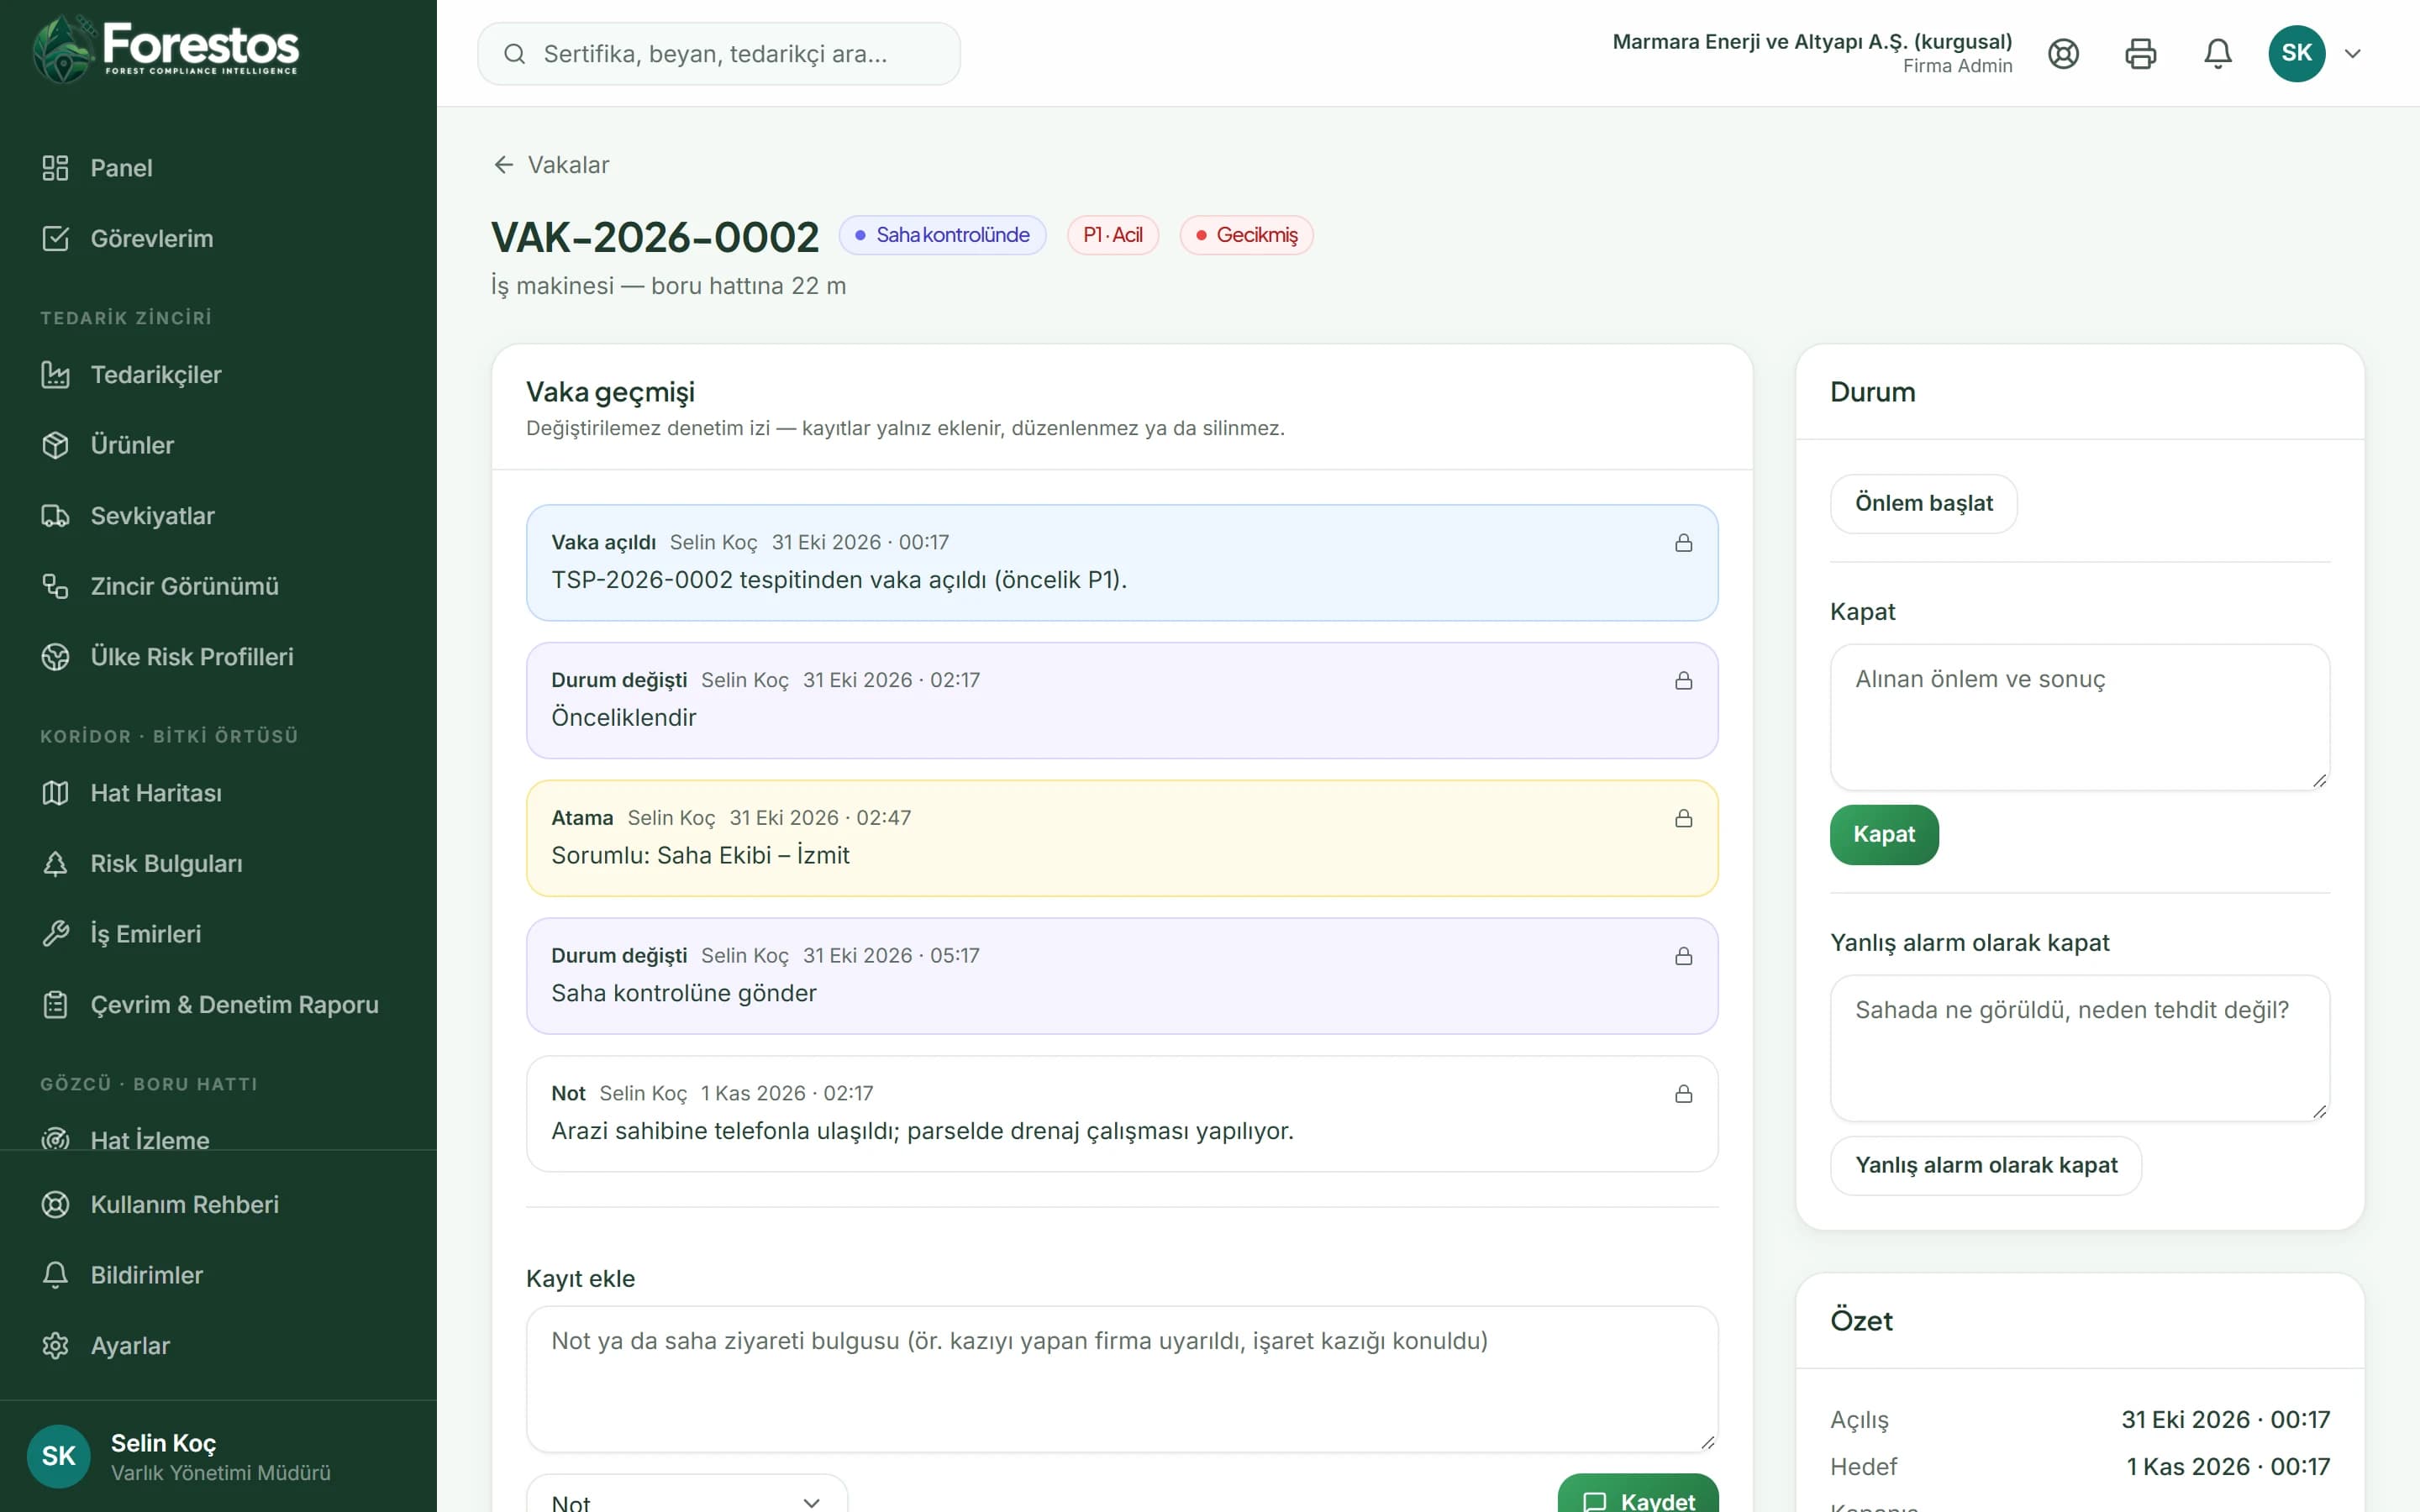
Every case goes through new → prioritised → field check → mitigation in progress → closed (or false alarm); every change is added to the timeline.
Change History Analysis
Reveal hidden patterns with time series
A before/after table and summary: first sighting, last observation, area change and trend (growing, stable, shrinking).
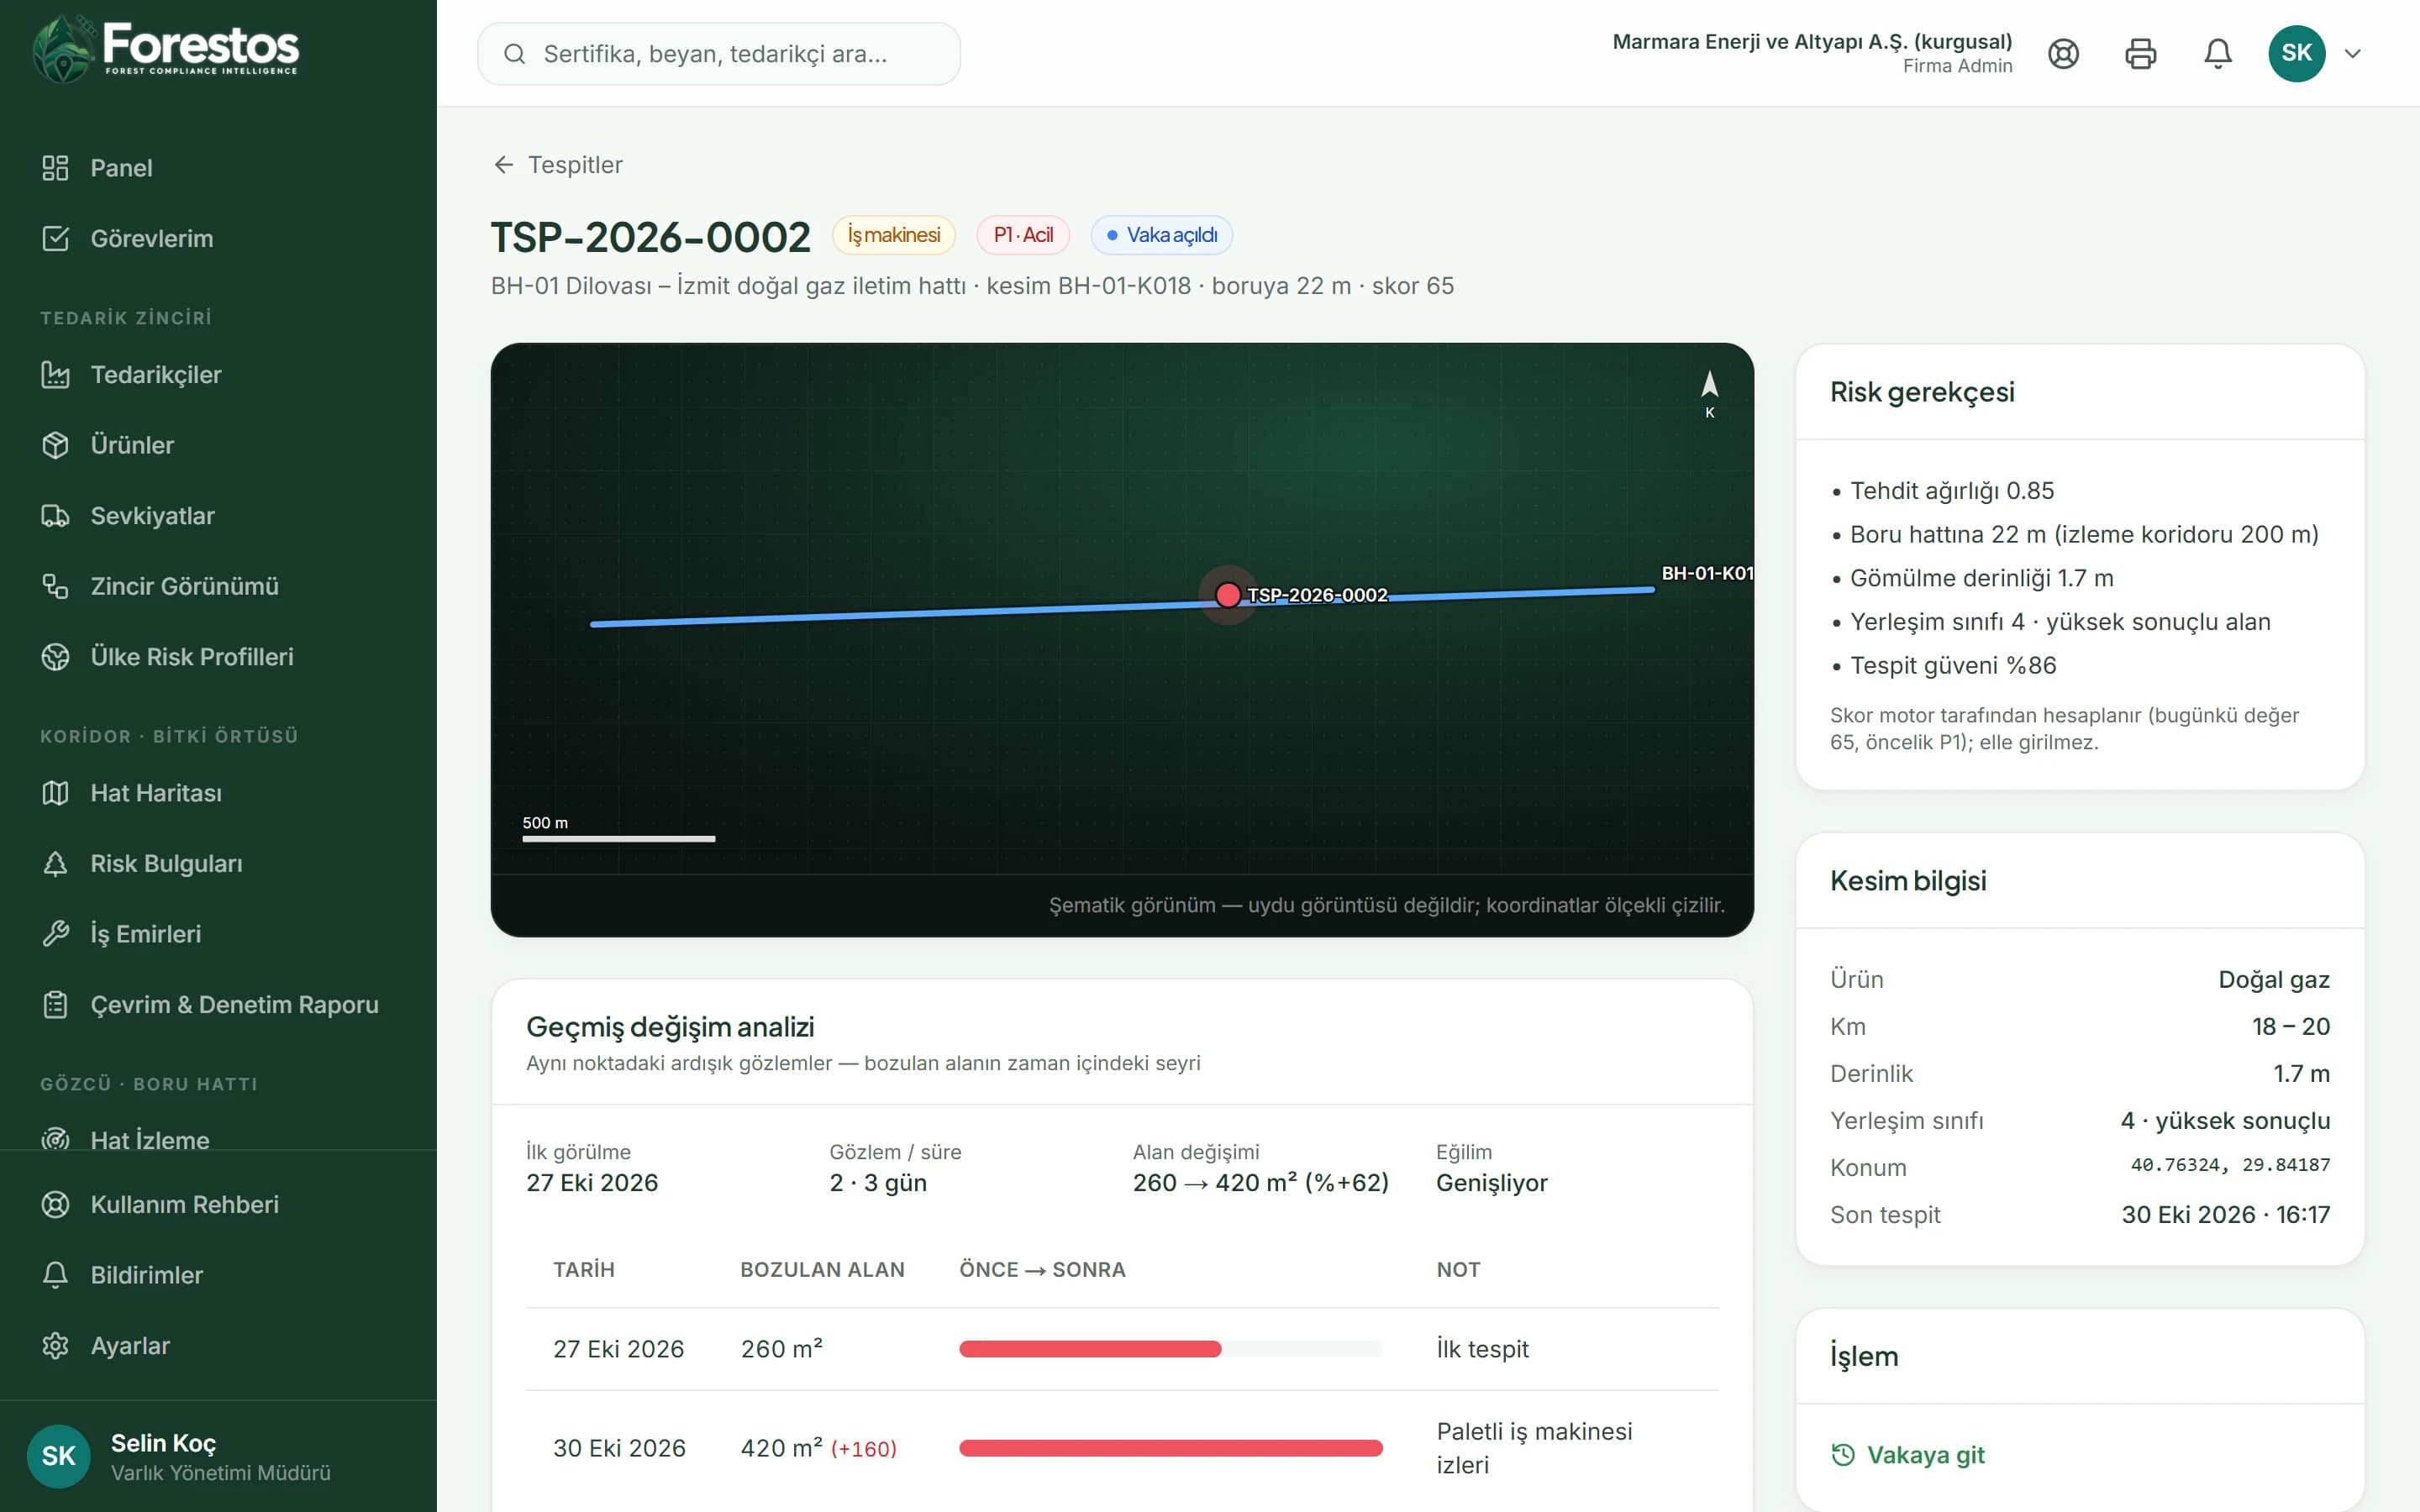
Be ready for an audit at any time
Frequently asked questions
Frequently asked questions: Regulatory & audit compliance.
Would you like a short introductory call?
Get in touchCan the records be changed?
The case timeline is append-only; an existing record cannot be changed.